Prepare with Microsoft : SC-200 exam braindumps as your best preparation materials

Last Updated: Nov 01, 2026
No. of Questions: 435 Questions & Answers with Testing Engine
Download Limit: Unlimited
Professional & latest exam products for SC-200 Exam Passing
Our professional & latest exam products of BraindumpQuiz SC-200 exam quiz braindumps can simulate the real exam scene so that you know the exam type deeper. Then repeated practices make you skilled and well-prepare when you take part in the real exam of BraindumpQuiz SC-200. Our three versions of SC-200 quiz torrent materials make everyone choose what studying ways they like.
100% Money Back Guarantee
BraindumpQuiz has an unprecedented 99.6% first time pass rate among our customers.  We're so confident of our products that we provide no hassle product exchange.
- Best exam practice material
- Three formats are optional
- 10 years of excellence
- 365 Days Free Updates
- Learn anywhere, anytime
- 100% Safe shopping experience
- Instant Download: Our system will send you the products you purchase in mailbox in a minute after payment. (If not received within 12 hours, please contact us. Note: don't forget to check your spam.)
Microsoft SC-200 Practice Q&A's

- Printable SC-200 PDF Format
- Prepared by SC-200 Experts
- Instant Access to Download
- Study Anywhere, Anytime
- 365 Days Free Updates
- Free SC-200 PDF Demo Available
- Download Q&A's Demo
Microsoft SC-200 Online Engine

- Online Tool, Convenient, easy to study.
- Instant Online Access
- Supports All Web Browsers
- Practice Online Anytime
- Test History and Performance Review
- Supports Windows / Mac / Android / iOS, etc.
- Try Online Engine Demo
Microsoft SC-200 Self Test Engine

- Installable Software Application
- Simulates Real Exam Environment
- Builds SC-200 Exam Confidence
- Supports MS Operating System
- Two Modes For Practice
- Practice Offline Anytime
- Software Screenshots
Your information deserves the same protection as your money. BraindumpQuiz runs a strict data safety system for every SC-200 buyer in 2026, so preparing for the Microsoft Security Operations Analyst never means trading away your privacy.
Microsoft SC-200 Exam Overview:
| Certification Vendor: | Microsoft |
|---|---|
| Exam Name: | Microsoft Security Operations Analyst |
| Exam Number: | SC-200 |
| Real Exam Qty: | 40-60 |
| Exam Price: | $165 USD |
| Certificate Validity Period: | 1 year (renewal required) |
| Available Languages: | Chinese (Simplified), Korean, Japanese, English |
| Passing Score: | 700 (scale of 100-1000) |
| Exam Format: | Multiple-choice, Multiple-select, Case study |
| Exam Duration: | 120 minutes |
| Related Certifications: | Microsoft Certified: Security Operations Analyst Associate |
| Sample Questions: | DOWNLOAD DEMO |
| Exam Way: | Online proctored or in-person testing center |
| Pre Condition: | Microsoft recommends having experience with Microsoft 365 Defender workloads, security operations, and incident response. Knowledge of Azure Active Directory, basic networking, and scripting is beneficial but not mandatory. |
| Official Syllabus URL: | https://learn.microsoft.com/en-us/certifications/exams/sc-200 |
Microsoft SC-200 Exam Syllabus Topics:
| Section | Weight | Objectives |
|---|---|---|
| Mitigate threats using Microsoft Defender for Endpoint | 25-30% | - Configure Microsoft Defender for Endpoint environment
|
| Mitigate threats using Microsoft Defender for Identity | 15-20% | - Hunt threats using Defender for Identity
|
| Mitigate threats using Microsoft 365 Defender | 25-30% | - Hunt threats in Microsoft 365 Defender
|
| Mitigate threats using Microsoft Defender for Cloud Apps | 20-25% | - Configure Microsoft Defender for Cloud Apps
|
Key Facts About the SC-200 Exam and BraindumpQuiz's Service
The current exam information lists 40-60 questions for the SC-200 exam, with 120 minutes minutes allowed. Practicing against the clock at home builds the pacing habits that exam day rewards.
The Microsoft Security Operations Analyst blueprint covers these main domains:
- Mitigate threats using Microsoft Defender for Identity (15-20%)
- Mitigate threats using Microsoft 365 Defender (25-30%)
- Mitigate threats using Microsoft Defender for Cloud Apps (20-25%)
Additional domains complete the official outline, and our bank covers the full range.
Your money is protected by clear conditions. If you fail the corresponding exam within 60 days of purchase, send us a scanned copy of your enrollment slip and your official Score Report PDF within two days of the exam date; verified claims receive a full refund within seven days. The exclusions: exams taken within three days of purchase, a candidate name that does not match the payer, and free or expired products. If you prefer, we can exchange your product for two others of equal value instead.
Microsoft lists the following prerequisites for the Microsoft Security Operations Analyst: Microsoft recommends having experience with Microsoft 365 Defender workloads, security operations, and incident response. Knowledge of Azure Active Directory, basic networking, and scripting is beneficial but not mandatory..
Check the official certification page for the latest requirements before booking.
Because we remove the guesswork at every step. The SC-200 bank consolidates the Microsoft Security Operations Analyst knowledge points into expert-verified Q&As instead of leaving you to sift through the internet alone. A free demo shows the quality before you buy; instant delivery starts you the minute you do; 365 days of free updates — with a notification each time a new version releases — keep you current; and a strict information safety system plus a 7/24 golden-standard support team protect you throughout.
As of the latest information, the SC-200 exam requires a score of 700 (scale of 100-1000) to pass, and registration costs $165 USD. Microsoft sets both figures, so verify them on the official site when you book.
Upon successful payment, our system automatically emails the product to your mailbox and shows an instant download link — delivery typically takes about a minute. If nothing arrives within two hours, check your spam folder first, then contact our 7/24 support team. Installations are unlimited. Your purchase also includes 365 days of free updates: whenever we release a new version, we notify you to download it — no need to wait or worry about validity — and a 50% renewal discount applies when the period ends.
Microsoft Security Operations Analyst Sample Questions:
You have an Azure subscription that has Azure Defender enabled for all supported resource types.
You create an Azure logic app named LA1.
You plan to use LA1 to automatically remediate security risks detected in Defenders for Cloud.
You need to test LA1 in Defender for Cloud.
What should you do? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.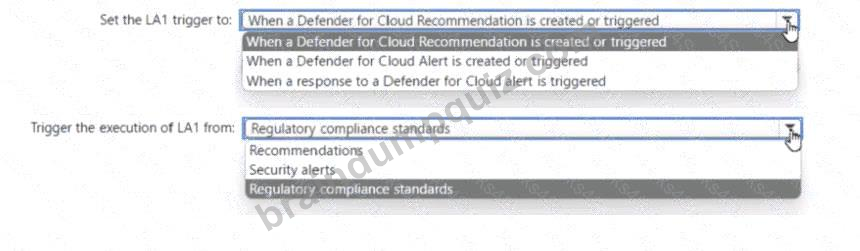
Correct Answer:

Explanation:
According to Microsoft Defender for Cloud automation documentation, Logic Apps can be integrated to automatically respond to recommendations or alerts. To test or automate remediation from Defender for Cloud, you must configure an automation workflow (Logic App) that triggers when a recommendation is created or updated.
Microsoft defines the available triggers for Defender for Cloud automation as follows:
When a Defender for Cloud Recommendation is created or triggered - This event type initiates the Logic App whenever a new security recommendation appears or an existing one changes state. It's the proper trigger for remediation scenarios because recommendations typically indicate a detected security misconfiguration or risk requiring action.
When a Defender for Cloud Alert is created or triggered - This applies to security alerts, not recommendations.
When a response to a Defender for Cloud alert is triggered - Used for incident-response workflows, not for testing remediation logic.
In the context of the question, the goal is to test automatic remediation for detected configuration issues (security risks). Those are surfaced as recommendations within Defender for Cloud, not as alerts.
Next, the execution source should be configured under:
Trigger the execution of LA1 from: Recommendations
This ensures that Defender for Cloud will execute the Logic App (LA1) automatically when relevant recommendations are triggered, allowing immediate testing and validation of the remediation logic.
In summary:
To test the Logic App remediation workflow in Defender for Cloud, you must:
Set the trigger type to "When a Defender for Cloud Recommendation is created or triggered".
Configure it to execute from "Recommendations".
Thus, the verified correct answers are:
# Set the LA1 trigger to: When a Defender for Cloud Recommendation is created or triggered
# Trigger the execution of LA1 from: Recommendations
You need to implement the Defender for Cloud requirements.
Which subscription-level role should you assign to Group1?
- A. Owner
- B. Contributor
- C. Security Assessment Contributor
- D. Security Admin
Correct Answer: C 🗳️
Explanation: Only visible for BraindumpQuiz members. You can sign-up / login (it's free).
You have a Microsoft Sentinel workspace named WS1. WS1 uses a Linux log forwarder that is Azure Arc- enabled. The forwarder receives logs from multiple network appliances. Some appliances send Common Event Format (CEF) messages, and other appliances send plain Syslog messages. Network appliances use a single Syslog facility.
You need to configure data ingestion to meet the following requirements:
* Duplicate ingestion must be prevented.
* Changes to the network appliances must be minimized.
* Plain Syslog events must be stored in a table named Syslog.
* CEF events must be stored in a table named CounonSecurityLog.
* The solution must use an API-based Azure Monitor Agent method that has a data collection rule (DCR).
What should you do?
- A. Configure all the appliance logs to use only the Microsoft-Syslog stream.
- B. Add an ingestion-time transformKql property to the Syslog data flow to exclude CEF-formatted events.
- C. Set the Syslog data source to a lower minimum severity level than the CEF data source.
- D. Configure separate facilities for CEF and Syslog devices in the DCR.
Correct Answer: B 🗳️
You have a Microsoft Sentinel workspace named workspace1 and an Azure virtual machine named VM1.
You receive an alert for suspicious use of PowerShell on VM1.
You need to investigate the incident, identify which event triggered the alert, and identify whether the following actions occurred on VM1 after the alert:
The modification of local group memberships
The purging of event logs
Which three actions should you perform in sequence in the Azure portal? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.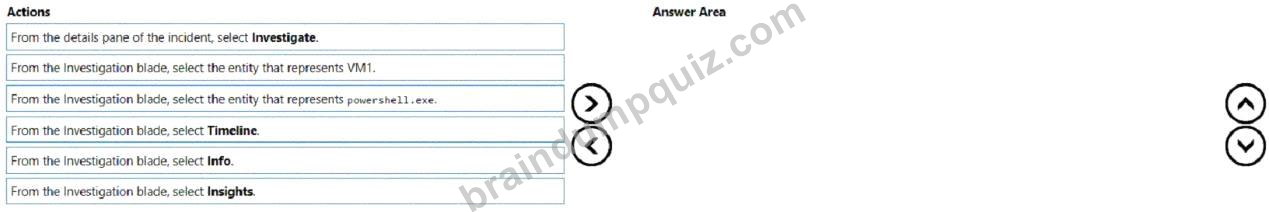
Correct Answer:

Explanation:
Step 1: From the Investigation blade, select Insights
The Investigation Insights Workbook is designed to assist in investigations of Azure Sentinel Incidents or individual IP/Account/Host/URL entities.
Step 2: From the Investigation blade, select the entity that represents VM1.
The Investigation Insights workbook is broken up into 2 main sections, Incident Insights and Entity Insights.
Incident Insights
The Incident Insights gives the analyst a view of ongoing Sentinel Incidents and allows for quick access to their associated metadata including alerts and entity information.
Entity Insights
The Entity Insights allows the analyst to take entity data either from an incident or through manual entry and explore related information about that entity. This workbook presently provides view of the following entity types:
IP Address
Account
Host
URL
Step 3: From the details pane of the incident, select Investigate.
Choose a single incident and click View full details or Investigate.
Reference:
https://github.com/Azure/Azure-Sentinel/wiki/Investigation-Insights---Overview
https://docs.microsoft.com/en-us/azure/sentinel/investigate-cases
You have an Azure subscription that contains a user named User1 and a Microsoft Sentinel workspace named WS1.
You need to ensure that User1 can enable User and Entity Behavior Analytics (UEBA) for WS1. The solution must follow the principle of least privilege.
Which roles should you assign to User1? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Correct Answer:

Explanation:
Microsoft Entra role: Security Administrator
Role for WS1: Microsoft Sentinel Contributor
To enable User and Entity Behavior Analytics (UEBA) in Microsoft Sentinel, a user must have permission to configure data connectors that access Microsoft Entra ID (Azure AD) identity data and to manage Sentinel settings for the workspace.
This requires roles in two scopes:
1## Microsoft Entra ID (directory) level - for identity data access.
2## Sentinel workspace level - for Sentinel feature management.
According to Microsoft documentation, enabling UEBA requires connecting Microsoft Sentinel to Microsoft Entra ID to import user and identity behavior data.
The Security Administrator role grants the necessary read permissions to user and sign-in data while still adhering to the principle of least privilege.
The Global Administrator role would also work but provides excessive privileges beyond what's required for UEBA configuration.
The Security Operator role is limited to viewing alerts and cannot configure Sentinel connectors.
Hence, Security Administrator is the correct least-privilege directory role.
To manage Sentinel configuration and enable features such as UEBA, data connectors, and analytics rules, the Microsoft Sentinel Contributor role is required at the workspace level.
The Sentinel Contributor role allows enabling/disabling features, managing playbooks, and configuring connectors.
The Sentinel Automation Contributor role is only for playbook automation permissions.
The basic Contributor role can manage Azure resources but doesn't grant Sentinel-specific privileges.
# Final Answer:
Microsoft Entra role: Security Administrator
Role for WS1: Microsoft Sentinel Contributor
Viewing page 1 out of 87 pages.
Viewing questions 1-5 out of 435 questions.
It is so easy for us to pass SC-200 exam after using your exam dumps, thanks for your great help.
 Griffith
Jesse
Marico
Harley
Most of the questions are from your SC-200 material.
Julian
Maurice
BraindumpQuiz is the world's largest certification preparation company with 99.6% Pass Rate History from 59430+ Satisfied Customers in 148 Countries.

Over 59430+ Satisfied Customers